Monitor AWS VPC tunnels using AWS transit gateway
Provide visibility into the connection status of onboarded AWS VPC VPN tunnels using AWS Transit Gateway and enable on-demand connectivity checks within the management platform.
Amazon Web Services (AWS) Transit Gateway acts as a cloud router. It connects enterprise virtual private clouds (VPCs) to AWS VPCs through a central hub, which allows for simplified peering relationships.
Security Cloud Control Firewall Management allows you to monitor the connection status of your onboarded AWS VPCs using AWS Transit Gateway.
Before you begin
Follow these steps to monitor AWS VPC tunnels using AWS Transit Gateway:
Procedure
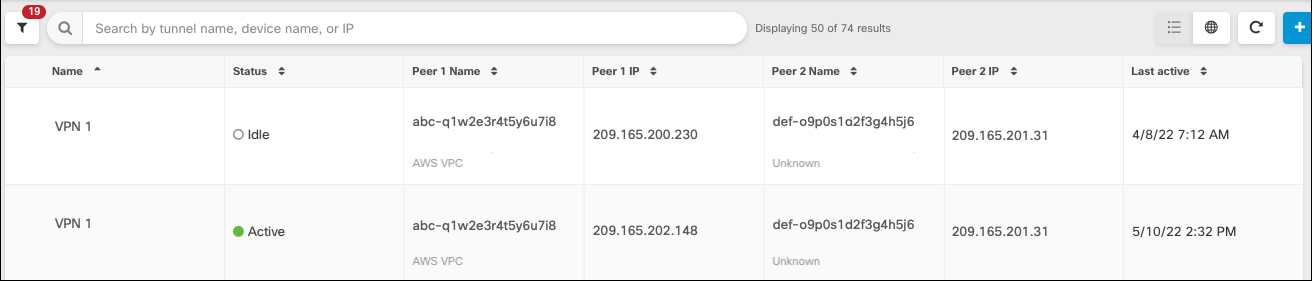
Step 1 | Choose . The VPN Tunnels page displays the connection status for all network tunnels managed by your Security Cloud Control tenant. The connection status for the VPN tunnel can be active or idle. | ||
Step 2 | Select a VPC, and then under Actions, click Check Connectivity. This triggers a real-time connectivity check against the tunnel and identifies whether the tunnel is currently active or idle. If you do not click the on-demand connectivity check link, a check across all tunnels on all onboarded devices occurs every ten minutes.
|
The VPN tunnel status for AWS VPCs is displayed on the VPN Tunnels page as active or idle. If you do not run an on-demand check, the system checks all onboarded tunnels every ten minutes. A notification appears when a tunnel goes down; none appears when it comes back up.